Reviews Sweet Security
Sweet Security Review: Virtual Patching for Cloud Runtime Security
At a glance
Sweet Security released virtual patching in October 2026 to deliver immediate runtime blocking of exploits in cloud and AI workloads through eBPF sensors without code changes.
Sweet Security review shows that the company added virtual patching to its runtime security platform on October 19, 2026. The feature lets teams apply one-click policies that block exploitation attempts against known CVEs or zero-days in live applications. No restarts or code modifications are required.
Sweet Security Platform and Virtual Patching Overview
Sweet Security, founded in Tel Aviv in 2023, operates a runtime-first CNAPP platform that uses lightweight eBPF sensors. The sensors deliver visibility, detection, and response across cloud workloads and AI agents. The company has raised roughly $126 million and processes more than one billion events daily while reporting over 99 percent accuracy on verified findings.
Virtual patching extends this platform by letting users select a vulnerability in the Sweet Vulnerabilities Catalog and enforce runtime protection. The catalog prioritizes issues with a Sweet Score based on reachability, exposure, and exploitability. Once selected, the policy deploys to affected nodes and follows workloads during scaling or restarts. Protection can be removed after a permanent fix is applied.
The feature addresses shrinking windows between vulnerability disclosure and exploitation, especially in environments using AI. It complements standard patching rather than replacing it. Sweet also offers a 30-day free Safety Net program that supplies sensors and policies for organizations affected by specific high-profile issues such as HTTP2Shell or Node2Shell.
Runtime Protection Features, Workflow, and Comparisons
The workflow begins when Sweet Attack, the platform’s autonomous AI red-team agent, identifies exploitable paths from runtime data. Users then choose Respond and Enforce Protection to distribute the policy. This creates a continuous Attack-Fix-Defend loop. In one documented case involving CVE-2026-111497 in the Brotli decoder, Sweet blocked remote code execution by intercepting targeted syscalls such as clone() in vulnerable code paths across Node.js, Python, Envoy, Istio, and certain Go frameworks.
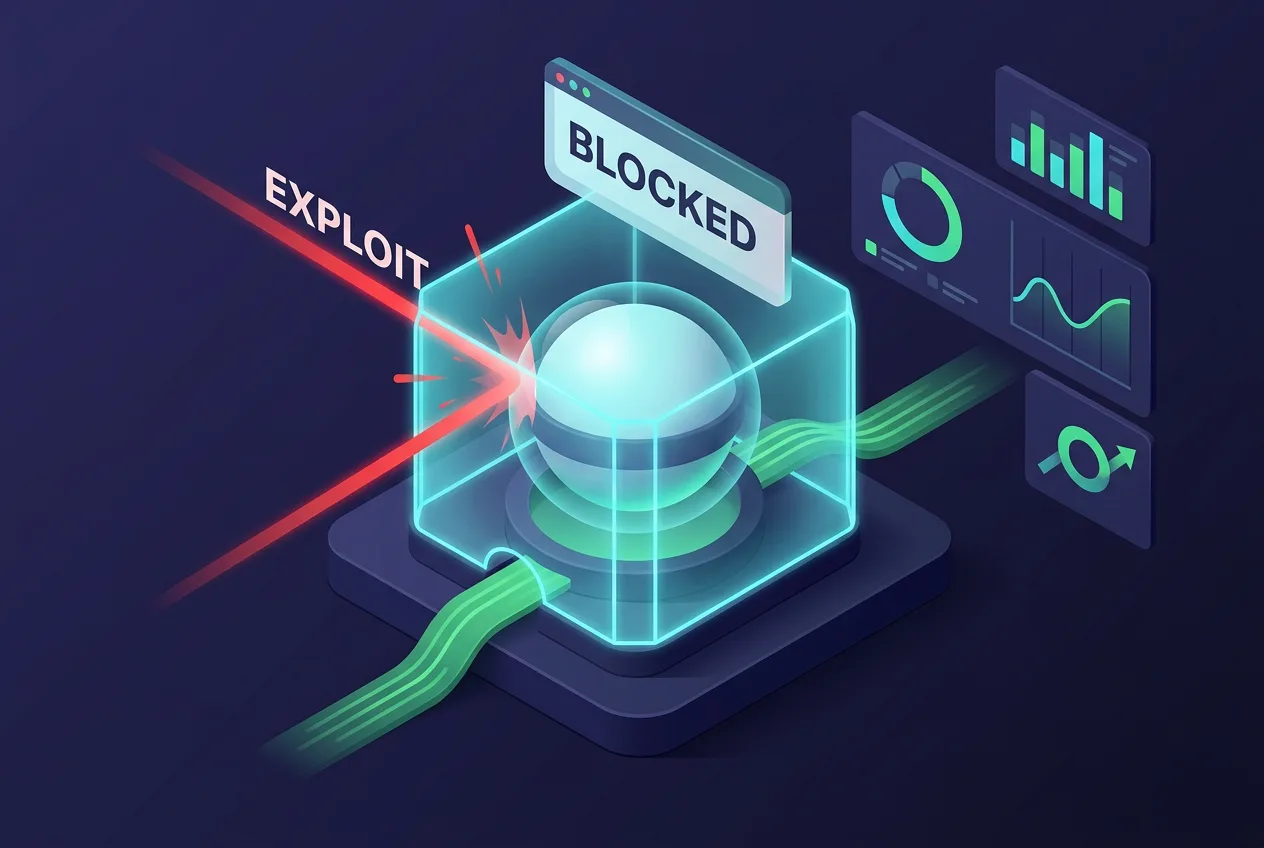
Key capabilities include support for custom code flaws in addition to known CVEs, automatic policy distribution to eBPF sensors, and zero downtime for legitimate traffic. The approach requires no redeployment of applications. Integration with Sweet Attack allows automated suggestions for policies based on continuous validation of exploit paths.
PeerSpot users have reported 80 to 90 percent reductions in vulnerability noise and 60 to 80 percent faster triage times after gaining runtime context. Some reviewers noted possible production overhead during initial deployment and requested stronger blocking options before the virtual patching release.
| Aspect | Sweet Security Virtual Patching | Traditional Patching | Agent-Based CNAPP Tools |
|---|---|---|---|
| Deployment time | Minutes via policy push | Hours to days | Minutes to hours |
| Code changes required | None | Usually required | None |
| Zero-day coverage | Yes via runtime rules | Limited until patch available | Partial via signatures |
| Production impact | Minimal, removable | Downtime possible | Variable by agent |
Compared with agent-based tools from competitors, Sweet relies on eBPF for lower overhead and combines vulnerability management with AI workload guardrails in a single platform. Traditional patching remains necessary for root-cause resolution, while virtual patching serves as an immediate mitigation layer.
Limitations, User Feedback, and Practical Considerations
Virtual patching depends on accurate runtime context; incomplete sensor coverage can leave some paths unprotected. The feature is new, so long-term data on sustained performance under heavy AI inference loads is still limited. Organizations must maintain sensors on all relevant nodes to ensure policy reach.
Public feedback before the October 2026 launch highlighted strong prioritization but occasional questions about blocking granularity in production. Sweet has not published formal pricing tiers for the add-on; access appears tied to existing platform subscriptions. The free 30-day Safety Net program provides an entry point for testing on specific threats without prior commitment.
Users considering adoption should verify eBPF compatibility with their kernel versions and container runtimes. Policies remain removable, reducing long-term risk if unexpected side effects appear. Continued integration between Sweet Attack and virtual patching is expected to expand automated coverage for zero-day scenarios in AI workloads.
Frequently asked questions
How does Sweet virtual patching differ from traditional updates?
Sweet virtual patching applies runtime policies through eBPF sensors to block exploit attempts without code changes or application restarts. Traditional updates require source modifications, recompilation, and redeployment that can take hours or days.
What workloads does Sweet Security support with virtual patching?
The feature covers cloud-native applications and AI workloads running on supported runtimes including Node.js, Python, Envoy, Istio, and select Go frameworks. Protection follows containers during scaling and restarts.
Is Sweet Attack required to use virtual patching?
Sweet Attack can suggest policies automatically from runtime data, but users can also select vulnerabilities manually from the catalog and enforce protection without the agent.
What are known limitations of Sweet virtual patching?
Coverage depends on sensor placement across all relevant nodes. The feature is recent, so extended performance data under sustained high-load AI scenarios remains limited. Kernel and runtime compatibility must be confirmed before rollout.
Filed under
Comments
No comments yet. Be the first!